Resolving SPF PermError and Strict DMARC DKIM Failures
Published:
22 Sep, 2026
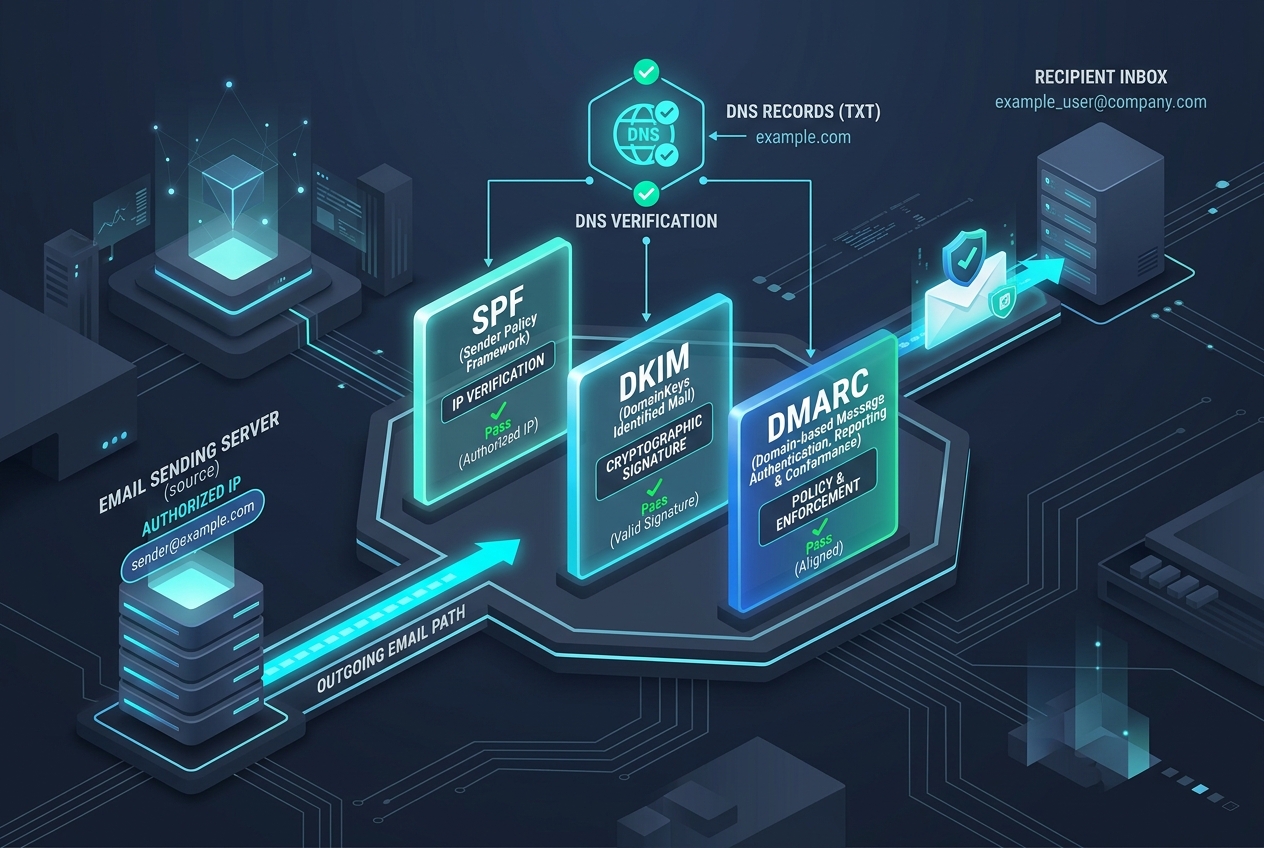
Root Causes of Email Authentication Breakdowns
Modern receiving Mail Transfer Agents (MTAs) like Google Workspace, Microsoft 365, and ProtonMail enforce strict validation pipelines combining RFC 7208 (SPF), RFC 6376 (DKIM), and RFC 7489 (DMARC). When sending volume scales or third-party SaaS vendors are integrated into an enterprise domain, subtle DNS misconfigurations trigger PermError, body hash mismatches, and identifier alignment drops. Resolving these issues requires inspecting DNS record structures, lookup tree depths, and cryptographic canonicalization rules.
1. SPF RFC 7208 Limit Violations and PermError
The most common failure in SPF evaluation is the 10-DNS-lookup limit specified in Section 4.6.4 of RFC 7208. When an MTA evaluates a sender's SPF record, each occurrence of the following mechanisms triggers a DNS query:
- include
- a
- mx
- ptr (deprecated)
- exists
- redirect
Mechanisms such as ip4, ip6, and all are static and do not trigger DNS resolution. Exceeding 10 DNS lookups forces an immediate PermError (Permanent Error), which DMARC evaluates as a definitive SPF fail.
Additionally, RFC 7208 mandates a strict limit of no more than 2 void lookups (queries returning NXDOMAIN or an empty NOERROR response). If legacy or typo-ridden vendor includes exist in the record, receiving servers abort evaluation.
# Check recursive SPF lookups using dig
dig +short TXT example.com | tr ' ' '\n' | grep include

# Trace nested includes for a specific vendor
dig +trace +short TXT _spf.salesforce.com
To eliminate lookup overflow without brittle manual CIDR flattening, administrators should prune deprecated third-party services, consolidate shared MX entries, or deploy dynamic macro-based DNS lookups using the exists mechanism for custom routing.
2. DKIM Body Hash Mismatches and Cryptographic Invalidation
A DKIM signature verification failure typically manifests in the Authentication-Results header as dkim=fail (bad signature) or dkim=fail (body hash did not verify). The parameter bh= contains the base64-encoded SHA-256 hash of the canonicalized email body, while b= is the cryptographic signature of the DKIM headers.
| Failure Mode | Technical Mechanism | Remediation Step |
|---|---|---|
| Canonicalization Mismatch | c=simple/simple fails if any intermediary MTA modifies whitespace, trailing line breaks, or tab characters. |
Enforce relaxed canonicalization: c=relaxed/relaxed in MTA signing configuration. |
| Header Modification | MTA or security gateway modifies a header listed in the h= tag (e.g., rewriting Subject or adding disclaimers). |
Sign only immutable headers; exclude dynamically rewritten headers from the h= list. |
| Public Key Truncation | 2048-bit RSA keys exceed the 255-character string limit in single-string TXT records. | Split the key into multiple quoted strings within the same DNS TXT resource record. |
For a 2048-bit RSA DKIM key, standard BIND and cloud DNS zone files require splitting strings longer than 255 octets:
; Correct multi-string formatting for 2048-bit DKIM in BIND zone format
default._domainkey.example.com. IN TXT ( "v=DKIM1; k=rsa; p=MIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEA0Y1+r..."
  "...second_half_of_public_key_string_here..." )
Validate the loaded public key directly against the operational selector:
# Query public key record for specific selector
dig +short TXT default._domainkey.example.com

# Verify key validity using opendkim-testkey (if installed)
opendkim-testkey -d example.com -s default -vvv
3. DMARC Identifier Alignment: Strict vs. Relaxed Modes
A passing SPF or DKIM result does not guarantee a DMARC pass. DMARC requires Identifier Alignment between the visible RFC 5322 From address and the authenticated domain identities:
- SPF Alignment: The domain in the
RFC 5321.MailFrom(Return-Path / Envelope Sender) must match the domain in theRFC 5322 Fromheader. - DKIM Alignment: The domain defined in the
d=tag of the DKIM-Signature header must match the domain in theRFC 5322 Fromheader.
By default, DMARC operates in relaxed mode (aspf=r; adkim=r), allowing subdomains to align with the apex organizational domain. When set to strict mode (aspf=s; adkim=s), an exact domain match is required.
# Strict DMARC Policy Record
_dmarc.example.com. IN TXT "v=DMARC1; p=reject; aspf=s; adkim=s; pct=100; rua=mailto:[email protected]; ruf=mailto:[email protected]"
Under strict alignment, if an automated transactional platform sends with Return-Path: [email protected] while the user sees From: [email protected], SPF alignment fails because mail.example.com does not exactly match example.com. In this scenario, DKIM must carry a valid signature with d=example.com to achieve overall DMARC compliance.
4. Verification Pipeline Checklist
- Count total DNS lookups across all SPF chains to guarantee the count is ≤ 10.
- Switch MTA DKIM canonicalization to relaxed/relaxed to prevent edge MTA body mutations from invalidating
bh=. - Audit third-party SaaS senders to verify custom Return-Path or aligned
d=DKIM selectors matching the root domain. - Inspect DMARC aggregate reports (RUA XML) for
disposition=rejectcaused by unaligned subdomain routing.