Fix DNS CNAME Coexistence Conflicts and Apex Errors
Published:
02 Oct, 2026
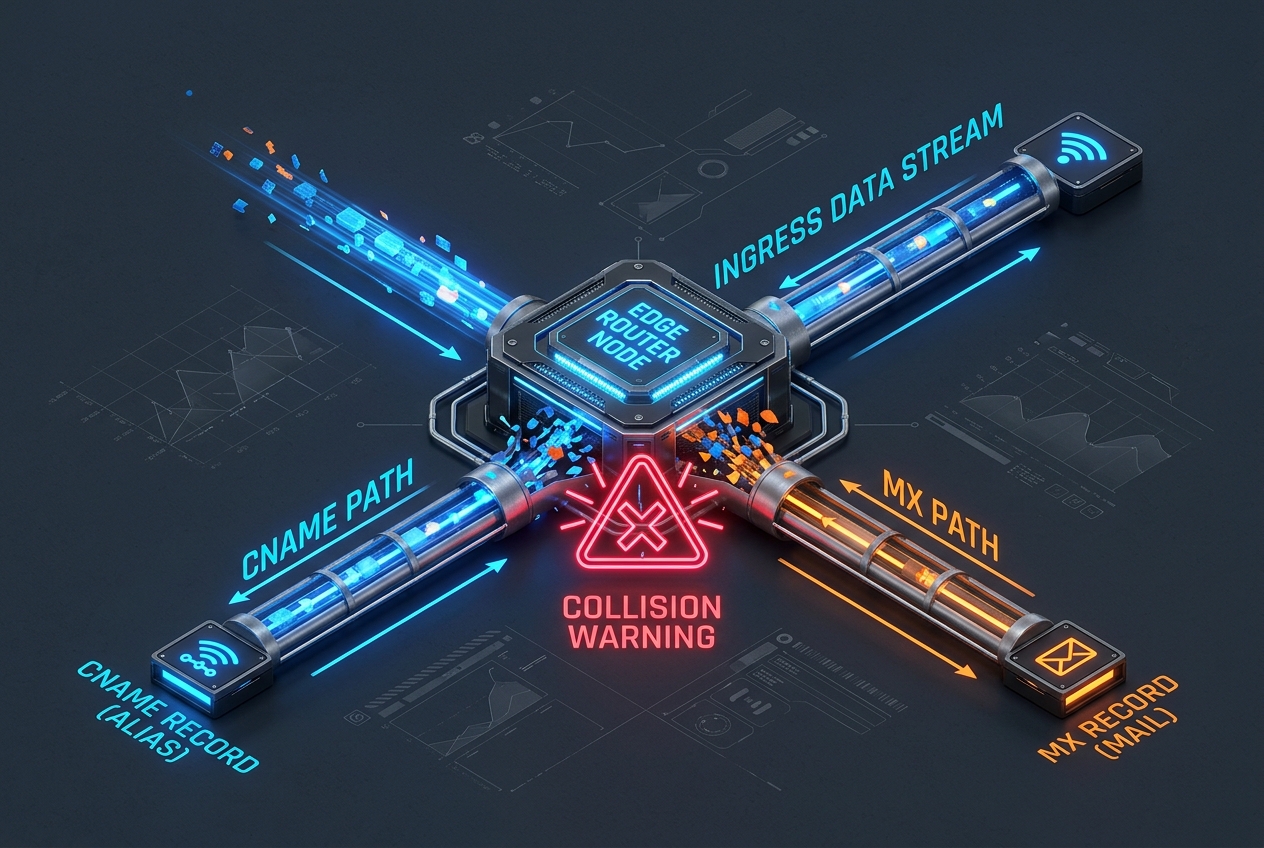
The Mechanics of CNAME Coexistence Violations
According to RFC 1034 (Section 3.6.2) and clarified in RFC 2181 (Section 10.1), if a CNAME (Canonical Name) record is present at a specific node (a fully qualified domain name), no other data records of any type (such as A, AAAA, MX, TXT, or NS) can exist at that exact same label. The sole exceptions are DNSSEC-related records like RRSIG and NSEC/NSEC3.
When administrators attempt to place a CNAME alongside other record types—most frequently at the zone apex (example.com alongside SOA and NS) or on a subdomain running dual services (e.g., pointing mail.example.com to a SaaS via CNAME while also defining an MX or TXT record)—authoritative and recursive DNS engines exhibit undefined, divergent behavior:
- Authoritative Servers (BIND9, PowerDNS, NSD): Authoritative daemons may fail to load the zone entirely or throw a
zone file syntax erroron reload. - Strict Resolvers (Unbound, Google Public DNS 8.8.8.8): When encountering a CNAME mixed with other records, resolvers may follow the alias and completely ignore sibling records like TXT (breaking SPF and DKIM) or return SERVFAIL.
- Permissive Resolvers: Some local caches return partial answers depending on which record was queried first, causing non-deterministic mail routing failures.
Detecting CNAME Conflicts with dig and Zone Validators
To identify whether a node has an invalid CNAME coexistence conflict, query the exact hostname for both the alias and the sibling record types.
# Query for CNAME at the target node
dig +noall +answer CNAME app.example.com

# Query for conflicting record types at the identical node
dig +noall +answer TXT app.example.com
dig +noall +answer MX app.example.com
If both queries return answers for the exact same FQDN, the zone violates RFC 2181. For BIND-managed authoritative systems, local validation can be executed using named-checkzone:
named-checkzone example.com /etc/bind/zones/db.example.comA syntax violation produces an explicit error:
/etc/bind/zones/db.example.com:24: app.example.com: CNAME and other data error
zone example.com/IN: loading from master file /etc/bind/zones/db.example.com failed: CNAME and other data
zone example.com/IN: not loaded due to errors.
To inspect remote behavior without running local zone files, use the InfoWebStats DNS Lookup tool to simultaneously evaluate all record sets returned across global authoritative nameservers. If the tool displays a CNAME alongside A, MX, or TXT records on the same label, resolvers will intermittently drop incoming traffic or fail email authentication checks.
Technical Solutions for CNAME Violations
1. Resolving Apex Domain Limitations
Because the zone apex (@) mandatory requires SOA and NS records, you cannot place a standard CNAME at example.com. Three standards-compliant patterns resolve this constraint:
| Method | Mechanism | RFC Compliance |
|---|---|---|
| ALIAS / ANAME Records | Authoritative nameserver resolves the target dynamically and serves synthesized A/AAAA records. | Fully Compliant (Client sees standard A/AAAA). |
| HTTPS / SVCB Records (RFC 9460) | Modern DNS clients query TYPE65 (HTTPS) at apex to obtain target aliases and IP hints directly. |
Native RFC Standard (Requires HTTPS-aware clients). |
| HTTP 301 Edge Redirect | Apex points to static edge IPs via A records; HTTP server issues 301 Moved Permanently to www.example.com. |
Fully Compliant (Standard HTTP routing). |
2. Separating Subdomain Service Records
A common mistake is configuring an email verification TXT record on a host that is also an alias to a third-party service provider:
; INVALID RFC CONFIGURATION
tracking.example.com.    300  IN  CNAME  thirdparty.saas.com.
tracking.example.com.    300  IN  TXT    'v=spf1 include:saas.com ~all'
To fix this, move the TXT and MX requirements to a dedicated subdomain or remove the CNAME in favor of direct IP mapping or provider-specific subdomain delegation:
; VALID SEPARATION
tracking.example.com.    300  IN  CNAME  thirdparty.saas.com.
em-tracking.example.com. 300  IN  TXT    'v=spf1 include:saas.com ~all'
Verification Workflow
After refactoring the zone records, clear local resolver caches and perform an authoritative trace query with dig:
dig +trace +nodnssec app.example.comConfirm that the authoritative answers return exclusively the canonical alias chain or the concrete address records without mixed responses. Run a secondary check on the InfoWebStats DNS Lookup interface to ensure that any conflicting TXT, MX, or address records have completely flushed from external authoritative caches.